
Passwordless Email Authentication: Magic Links, OTPs & Security
Published September 18, 2026 · Updated October 9, 2026
Passwordless email authentication lets you sign in to a website or app without entering a password for that service. Instead, the service sends a temporary login link or one-time verification code to your email address. You open the link or enter the code to complete sign-in.
Quick answer: How passwordless email login works
- Enter your email address on the website’s sign-in page.
- Request a magic link or one-time code.
- Open the email sent by the service.
- Click the login link or enter the verification code.
- Complete sign-in before the link or code expires.
Important: Passwordless email authentication is not automatically two-factor authentication. It typically relies on access to your mailbox as the primary sign-in proof. Protecting that mailbox is essential.
This guide explains email magic links, one-time passwords, security risks, implementation best practices, and how to fix common passwordless login problems.
What Is Passwordless Email Authentication?
Passwordless email authentication is a sign-in method that replaces a website’s traditional password prompt with an email-based verification step.
Instead of remembering another password, users prove that they can access the email address associated with their account.
The service then uses that proof to create an authenticated session.
Two common approaches are:
- Magic link authentication: The service sends a temporary URL that completes sign-in when opened.
- Email OTP authentication: The service sends a one-time code that the user enters on the sign-in page.
Both methods can reduce the need for users to create and manage passwords for individual services.
However, they introduce a different dependency: access to the registered mailbox.
What Does Passwordless Email Login Actually Verify?
A successful email challenge demonstrates that someone could access the message or code delivered to the specified address.
It does not necessarily establish:
- The person’s legal identity.
- Exclusive ownership of the mailbox.
- Whether the inbox is shared.
- Whether the email account has been compromised.
- Whether the user should receive administrative permissions.
For example, if three employees share the same support inbox, each may be able to receive a passwordless login link sent to that address.
For services requiring individual accountability, use separate user identities and appropriate access controls.
Is Passwordless Email Authentication the Same as Email Verification?
No.
Email verification typically confirms that an address can receive messages, often during account registration.
Passwordless authentication uses an email challenge as part of the actual sign-in process.
A service can verify an email address once during registration and continue using passwords afterward.
Another service can send a new magic link for every login.
These are different workflows, even though both involve clicking a link in an email.
Is Passwordless Email Authentication the Same as 2FA?
Not necessarily.
Two-factor authentication requires separate authentication factors under the service’s security design.
If a website only sends a magic link to your inbox, the email challenge may be its sole sign-in method.
If a website requires a password and then sends a verification code, that is a different flow, although the independence of the factors still matters.
For a deeper explanation, read our email two-factor authentication guide.
💡 Discover Helpful Guides: Email Authentication Outlook: Setup and Recovery
Follow the Sign-In Journey From Request to Session
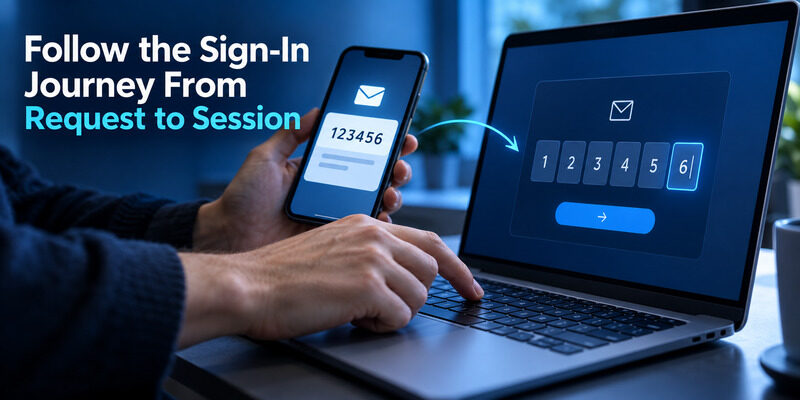
How Does Passwordless Email Authentication Work?
The exact user interface varies by provider, but most email-based passwordless flows follow a similar process.
Step 1: Enter Your Email Address
Open the legitimate website or application.
Select an option such as:
- Continue with email.
- Sign in with a magic link.
- Email me a login code.
- Passwordless sign-in.
Enter the email address registered with the service.
Make sure the website address is correct before submitting it.
Step 2: Request a Login Link or Code
The service creates a temporary authentication challenge.
Depending on the implementation, it may send:
- A one-time login URL.
- A short numeric code.
- An alphanumeric verification code.
The challenge should be associated with the intended account and sign-in attempt.
Step 3: Check Your Inbox
Open the email account you entered.
Look for the message from the service.
Check the sender and expected destination before opening the link.
If the message does not arrive immediately, check Spam, Junk, and filtered folders.
Avoid requesting many codes in rapid succession.
Step 4: Complete Verification
For a magic link:
- Open the email.
- Select the login link.
- Follow any additional browser confirmation.
- Return to the application if prompted.
For an email OTP:
- Read the code in the email.
- Return to the original sign-in screen.
- Enter the code.
- Submit it before expiration.
Some providers bind a magic-link request to the browser or device where the login started.
If the link opens in a different browser, the service may ask for additional confirmation or require you to return to the original session.
Step 5: Establish a Secure Session
After the service validates the challenge, it creates an authenticated session.
The browser or app may then maintain that session using secure cookies or another supported session mechanism.
Receiving an email does not mean login succeeded. The service must validate the challenge and establish the session.
A secure implementation should also ensure that a used or expired login token cannot be replayed.
Example: Signing In With an Email Magic Link
Imagine a user signing in to a project management application.
- They open the app’s official login page.
- They enter their registered email address.
- The app sends a magic link.
- They open the message in their inbox.
- They click the link.
- The app validates the challenge.
- They are signed in.
No password for that project management app is required during the normal flow.
However, if an attacker controls the user’s mailbox, they may be able to request and use the same type of login message.
That is why mailbox security is central to passwordless email authentication.
📖 Read More Guides: Email Authentication Failed Fixes for Login and Sending
Expect Different Behavior Across Browsers and Devices
Same-browser flows
Some implementations connect a challenge to browser state created when the user requested it. Opening the message in another browser can lose that state. Auth0’s documentation describes this restriction for its Classic Login magic-link flow, but it should not be generalized to every provider or every Auth0 configuration.
If passwordless email authentication fails after a link opens an unfamiliar browser, return to the original request and follow the service’s guidance. A mail app’s embedded browser can also behave differently from the browser where you started. Avoid repeated requests until you understand which screen owns the active attempt.
Cross-device flows
Other implementations explicitly support completion on another device after an additional check. Firebase’s email-link documentation, for example, describes confirming the email address when the original local state is unavailable. That is a designed flow, not permission to remove state checks from an unrelated implementation.
Test mobile-to-desktop and desktop-to-mobile journeys separately before launching a product. Include private browsing, expired sessions, and links opened by a default mail app. Passwordless email authentication should explain a recoverable mismatch in ordinary language: return to the original browser, confirm the address, or request a new link. A generic error gives users no way to distinguish an expired token from a valid token opened in the wrong context.
📖 Read More Guides: Email Authentication SPF Checks and Domain Setup Explained
Diagnose Delivery Delays Without Creating More Confusion
Verify that mail can reach the inbox
First confirm the address, spam folder, filters, forwarding, and mailbox capacity. Send an ordinary test message from an account you control if you need to establish whether the inbox receives mail at all. An authentication service cannot complete the user’s journey if the destination silently discards its messages.
Passwordless email authentication depends on transactional delivery, so product teams should monitor submission, provider acceptance, bounces, and complaint events separately. A successful API call to a mail service is not the same event as the user receiving a usable message.
Control resend behavior
The interface should explain when users may request another message and what happens to older challenges. Some implementations invalidate previous links; others allow a limited overlap. Follow the actual product behavior instead of promising that the newest message always cancels every older one.
| User observation | Likely investigation | Helpful action |
|---|---|---|
| No email arrives | Address or delivery | Check destination and filtering |
| Several messages arrive late | Multiple requests | Use the active attempt’s instructions |
| Link opens but sign-in fails | Token or browser state | Return to the request context |
| Mailbox itself is inaccessible | Mail account recovery | Recover the inbox first |
For a passwordless email authentication incident, record when the request was made and when the message reached the mailbox. Those two timestamps help separate a slow delivery from a token that was opened too late. Keep the message identifier if support requests it, but redact the usable link.
Keep resend controls rate-limited and avoid revealing whether arbitrary addresses have accounts. Passwordless email authentication can otherwise become a tool for flooding inboxes or discovering users. Give a neutral confirmation while recording sufficient internal evidence to diagnose failures without exposing account membership publicly.
📖 Read More Guides: Google Email Two Factor Authentication Setup for Gmail
Protect the Mailbox That Controls the Login
A person who controls your inbox may be able to request new login messages from connected services. Protect the mailbox with the strongest supported sign-in method you can maintain, and keep recovery options independent of the same device. Review forwarding rules and delegated access as well as the password.
Passwordless email authentication does not remove the need to secure the email account. It changes which account deserves particular attention. A strong password on a rarely used website cannot compensate for an inbox that remains accessible on a shared computer with an unattended session.
Treat a login link as a temporary credential. Do not forward it to support, coworkers, or another address simply because opening it elsewhere is convenient. An unexpected message may mean someone entered your address, but it does not by itself prove your account was compromised. Start any investigation from the service directly.
Unlike a passkey bound to a relying party, an email link can be copied and presented through misleading contexts. Passwordless email authentication therefore needs careful destination checks and suitable controls for sensitive actions. If the service asks for additional verification before changing a payout address or administrator role, that is a separate authorization boundary. Do not assume a successful mailbox challenge should unlock every action indefinitely.
💡 Discover Helpful Guides: Google Workspace Email Authentication for Business Domains
Keep Authentication Separate From Authorization
Establish a verified session
The authentication component decides whether the email challenge was accepted and which account it represents. Session management then maintains that identity across subsequent requests. Use the provider’s supported session mechanisms and verify tokens on trusted infrastructure when a backend relies on them.
OWASP’s Session Management Cheat Sheet discusses secure session handling, including cookie protections and session lifecycle controls. These remain necessary with passwordless email authentication. Removing a password field does not make session theft or insecure cookie handling irrelevant.
Enforce permissions on the server
A signed-in user should receive only the permissions assigned to that identity. Do not grant access because a browser sends an email address that looks like an employee address, or because a client-side flag says the mailbox was verified. Validate identity and authorization through the trusted server or access-control system.
Consider an invitation to a private project. The login establishes the user, while the invitation determines whether that user may join the project. Keep those checks separate and bind the invitation to its intended recipient. Passwordless email authentication can make the entry experience simple while the backend still enforces membership, role, and resource ownership. Test these boundaries with two accounts: one authorized and one signed in but uninvited. That comparison catches mistakes a successful happy-path demonstration will miss.
🗺️ Browse How-To Guides: Passwordless Email Authentication With Magic Links and Codes
Compare Email Links Codes and Passkeys
Choose a method according to the task rather than the number of clicks in a demo. Email links reduce typing but introduce browser and delivery dependencies. An that delivers codes makes the return to the original screen explicit, while still depending on mailbox access. Passkeys use a different mechanism and do not need a message to arrive for each sign-in.
| Method | Main dependency | Practical trade-off |
|---|---|---|
| Email link | Inbox and link handling | Convenient, but context can matter |
| Email code | Inbox and code entry | Clear screen handoff, extra typing |
| Passkey | Available credential and device flow | No email delivery dependency |
| Password plus authenticator | Password and enrolled code source | Separate second step to maintain |
Passwordless email authentication can suit low-frequency access where people already have a reliable inbox open. For frequent access, waiting for messages may become more frustrating than remembering a session or using a passkey. Evaluate the full journey, including recovery and shared-device use, before deciding that a shorter form is always easier.
A pilot should include people who check mail on a different device from the one they use for the application. Passwordless email authentication may look effortless in a developer’s single-browser test while creating several extra steps for those users. Observe that handoff before treating the design as finished.
For sensitive work, define the required assurance and the consequences of mailbox compromise. The choice may involve an identity provider, device controls, and additional verification rather than a simple link-versus-code preference. Passwordless email authentication is one building block in that design. It should be judged by who can obtain the challenge and what the resulting session is allowed to do.
📘 Find the Right Guide: Email Authentication SPF Checks and Domain Setup Explained
Plan for Lost Inbox Access and Address Changes
Recover through an independent route
If your inbox becomes inaccessible, a service that sends every login and recovery message to that same address can leave you stuck. Before depending on it for important accounts, inspect the supported recovery options. An existing session, another verified method, or a formal support process may help, but none should be assumed without checking.
For product teams, recovery should be designed alongside passwordless email authentication. A support agent must not change the registered address merely because someone knows the old one. Define how ownership is established and how high-risk changes are reviewed without asking people to disclose usable login tokens.
Change the address while access still works
Update the registered address before abandoning an old mailbox or leaving an organization. Follow the application’s confirmation process and verify the new destination. Keep the old account available until the change is complete and the next login succeeds.
Retain control of a custom domain
Consider all services tied to a custom domain before letting that domain expire. Receiving mail at an address is only reliable while you control its delivery. Passwordless email authentication can outlive the device on which it was first configured, but it cannot protect an account from an unmaintained destination. Keep an account inventory that lists the registered address and recovery method without storing active magic links or one-time codes in the same document.
💡 Discover Helpful Guides: Email Authentication in Zoho CRM With DKIM SPF and DMARC
Add an Authenticator When a Second Factor Is Available
Check what the service actually supports
Passwordless does not automatically mean multifactor. A link that proves mailbox access may be the only sign-in factor used by the application. Whether additional verification is available depends on the service’s design and policy. You cannot add an arbitrary authenticator entry and expect the website to recognize its codes.
If the provider offers standard time-based code enrollment, can generate those codes after you register its QR code or setup key. That gives you a supported second-step option where the account accepts it. It does not replace the application’s email-link mechanism or repair a lost inbox by itself.
Test the combined journey
When configuring an additional method, save the provider’s recovery codes first and keep the current session open. Complete the enrollment confirmation, then test a sign-in that actually asks for the new factor. The presence of an account label inside an app is not proof that the provider enabled the method.
Passwordless email authentication combined with another method should have understandable recovery behavior. Know whether losing the phone sends you back to the inbox, a recovery code, or an administrator. Avoid a circular setup in which the only way to open the inbox requires a code stored behind that same inbox login. Independent recovery makes the additional protection practical instead of fragile.
💡 Discover Helpful Guides: How to Add Email to Authenticator App With QR or Manual Setup
Frequently Asked Questions
Is passwordless email authentication always safer than a password?
No. Its security depends on mailbox protection, token handling, session controls, and recovery. It can remove password reuse at the application, but mailbox compromise may expose connected accounts. Compare the complete system instead of judging safety by whether the form contains a password field.
Can I open a magic link on another device?
Sometimes. The service may require the original browser or may provide a cross-device confirmation flow. Read the current prompt and provider instructions. If the link fails after changing devices, return to the original request before generating several more messages or assuming your account is locked.
Are email codes the same as authenticator codes?
No. Email codes are delivered through a mailbox, while an enrolled authenticator generates codes from a shared secret. The service decides which type it accepts at a particular prompt. Typing an authenticator code into an email verification field will not complete an unrelated challenge.
Can a shared inbox support individual user accounts?
It can receive login messages, but everyone with access may be able to use them. That weakens individual accountability and complicates recovery. Use separate identities for people when permissions, audit history, or sensitive data need to remain associated with a specific employee or customer.
What should I do with an unexpected login email?
Do not use or forward its link. Open the service independently if you want to review account activity. Someone may have entered your address by mistake, so the message alone does not prove compromise. Investigate repeated unexpected requests and check mailbox security without disclosing any active challenge.
🗺️ Browse How-To Guides: How to Add Email to Microsoft Authenticator
Final Thoughts
Passwordless email authentication offers a direct sign-in route through a mailbox you already use. The experience works best when the destination is reliable, the message explains its purpose, and the service handles expiry, browser context, and recovery clearly. A missing password field is only the visible part of that system.
As a user, begin from the genuine service, check the destination address, and keep login links private. Protect your inbox and review its recovery methods before using it as the entry point to important accounts. If a link fails, distinguish delivery, expiry, and browser-state problems instead of repeatedly requesting replacements without checking the current attempt.
As a developer, design passwordless email authentication around a controlled challenge lifecycle and a securely established session. Test unauthorized resource access as carefully as successful login. Keep identity proof separate from membership and administrative permissions, and make account recovery resistant to casual address-change requests.
Where a service supports standard authenticator enrollment, Authenticator App can provide its accepted second-step codes. Configure that method through the service itself and verify the combined login journey. Choose email links, codes, passkeys, or additional factors according to the access you need to protect and the recovery you can maintain. The result should be a sign-in process people understand even when an email arrives late or their usual device is unavailable.
Download Authenticator App
Secure your accounts with fast, reliable two-factor authentication. Download now and protect your login in seconds.
