
What Is OTP and Which Code Should You Use?
Published November 16, 2026
By the Authenticator App Team
Last updated: November 2026
An OTP is a one-time password that a service accepts for a single verification. Depending on the sign-in, it may arrive by text or email, appear in an enrolled authenticator, or come from a hardware token. Check the wording beside the input box before typing anything. A code from the wrong channel can look perfectly valid and still fail.
If you received a code you did not request, leave it unused and open the service directly to check your account. If you did request it and the code has expired, return to the active challenge and get a fresh value from the method it names. The tables below show where to look and what to try when the code is missing.
What an OTP Proves During Sign-In
OTP authentication checks that the person completing a challenge can supply a valid short-lived value. The service can use the value alongside a password, as part of a passwordless flow, or to confirm a particular account action. The fact that a screen says OTP does not tell you whether the whole flow uses two different factors. You need to know what else the service verifies and which channel provides the code.
Check What the Code Is Tied To
A delivered verification code may be tied to one sign-in request or to a particular action, such as verifying a phone number. An OTP code from a time-based authenticator works differently. The app and service use enrollment data and the current time to compute corresponding values. The digits on a text message and those in the app can be the same length without having the same purpose.
Separate the Current Code From Setup Information
A TOTP setup key or QR code lets an authenticator calculate future values. The active code is only the value the provider currently asks you to enter. Keep the setup key in a trusted authenticator and the current code within the active provider challenge. A recovery code issued earlier may be valid only in the provider’s alternate sign-in flow. The source of the information tells you more than the way it looks.
Find the Correct OTP Source
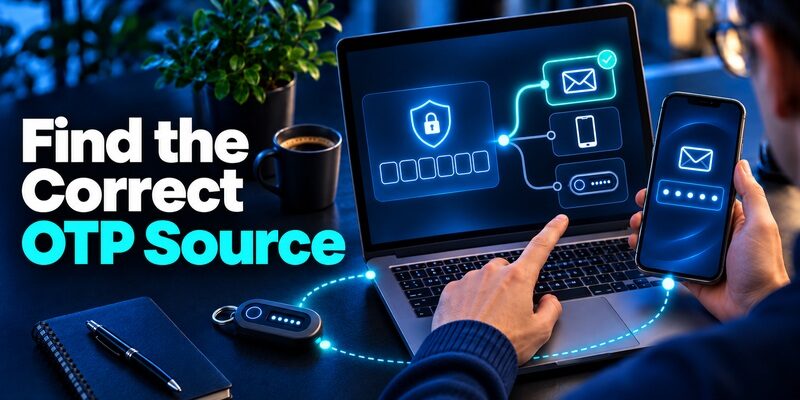
Read the current challenge from top to bottom before requesting another code. If the site shows a partially hidden destination, compare it with the phone number or inbox you actually control. If it names an authenticator, open the enrolled app and check the exact account. Follow a hardware or approval prompt as described by the service.
| Prompt or label | Where to look | What to confirm |
|---|---|---|
| Text message or SMS | The registered number | It belongs to the active request |
| Email verification | The registered inbox | The destination and service match |
| Authenticator app code | Your enrolled account entry | The timer and account label match |
| Hardware token code | Your registered device | It generates codes rather than asking for a touch |
| Backup or recovery code | Your securely stored recovery copy | Use the provider’s separate recovery prompt |
Confirm the Account and the Action
An OTP login page may show an email address, organization name, or partially hidden phone number. Check those clues before searching for the code. If you were changing a setting and the message instead says someone is signing in, leave that code unused. Close the prompt and verify what happened directly in the account.
Keep One Challenge Active
If the service offers resend, wait long enough to check the first message before you use it. A resend or a restart may create a new challenge. Use the code that belongs to the prompt you intend to finish. If the messages arrive out of order, compare their timestamps and follow the service’s instructions rather than trying every value in sequence.
Some screens ask for a number shown in a browser to be entered into an enrolled app instead of asking you to copy one back to the browser. Read the direction of the prompt. If the service says to approve a request, find it on the device you previously registered and make sure it corresponds to the session you started.
How SMS OTP and Email OTP Differ
With an SMS OTP, the service sends a message to the number it has on file. With an email OTP, it sends a message to the relevant inbox. These methods depend on delivery and access to the destination. A carrier problem can delay texts, and an inbox filter can hide mail. Neither problem is fixed by opening an unrelated code generator.
When a Text Does Not Arrive
Check that the final digits shown on the sign-in page belong to your current number. Confirm the phone can receive messages. If the number is old or unavailable, select an approved alternate method or use the service’s recovery flow. Repeatedly requesting a new OTP will not bring back a number you no longer control.
When the Email Is Missing
Check that you are in the correct inbox. Look at filters, spam, and the mail app’s account selector. An OTP email may arrive while you are viewing another mailbox. If it does not arrive and the service lets you use another enrolled method, choose that method. Keep the email account itself recoverable when it holds verification messages for other services.
The FTC’s consumer advice describes impostors who ask people to read back a verification code. Type a delivered code only into the genuine service for a request you started. A caller claiming to cancel an account problem does not need the number from your text message.
Why an App OTP Can Work Without a Message
An authenticator already enrolled for TOTP calculates codes from a shared secret and the current time. RFC 6238 defines the default time step as 30 seconds. The service can check the code when you submit it. A matching app entry does not need to receive an SMS or look up the code from the account provider each time.
Check the App Entry Before You Type
Open the entry matching the exact email or account named on screen. A personal and work account can share a brand icon while using different secrets. If the timer is nearly over, wait for the next code. Give yourself enough time to enter and submit the full value without racing the countdown.
Keep Offline Generation and Online Sign-In Separate
Google Account Help confirms that Google Authenticator can generate codes without internet or mobile service. The browser or app signing into the account still has to connect to the provider. If the phone has been offline for a while and several codes fail together, check its system time. If just one entry fails, check which enrollment the service accepts.
If the app allows copying, verify the entry before you copy and the browser tab before you paste. A clipboard may still hold a code from your previous sign-in. When you are unsure whether it is current, return to the correct app entry and read the newly displayed value.
Fix an Expired or Rejected OTP
Start by reading the error. A value can be expired because the value changed, because the sign-in challenge itself ended, or because the service replaced it after a new request. A rejection can also mean the account or method is wrong. Keep any session that still works until you know how to recover.
| Symptom | First check | Next step |
|---|---|---|
| Code changes as you enter it | App countdown | Wait for a new interval |
| Several app entries fail | System date and time | Use automatic time and retest |
| One entry fails after a phone change | Registration and account label | Use a working fallback and verify the enrolled method |
| Latest text arrives after page was closed | Whether the challenge is still active | Start a new request at the official service |
| Page expects a different factor | Method named beside the field | Select the supported factor you actually have |
Retry Once With a Fresh Value
Open a new provider challenge if the old page timed out. For an app, check the timer and the active account. For a message, use the value linked to the request that is still open. An OTP entered into a different kind of challenge will keep failing even if it is current.
Use a Fallback Before Removing Anything
If the next attempt fails, look for the service’s alternate verification option. Use a registered key, backup code, or another trusted device where supported. When the original factor is gone, follow official recovery. Deleting an app entry does not tell the provider to stop asking for that OTP or register a replacement.
When a service has several verification modes, pay attention to what you selected on the last screen. Choosing an app-code prompt and then requesting a text can leave a value on your phone that belongs to a different prompt. Return to the service’s method selector and pick the one you intend to use.
Handle an Unexpected OTP Without Sharing It
An unexpected verification message can reflect a mistake or a login attempt. Its arrival alone does not identify who requested it or establish that somebody successfully entered the account. Leave the value unused. Open the service from an address or app you already trust and review account activity where the provider offers it.
If Someone Asks You to Read the Code
End the interaction and use an established support number or account channel. The FTC warns that scammers may present themselves as a bank, service provider, or support representative. Treat the OTP as proof for the service’s own form. If you entered it into a fake page, follow the provider’s instructions for securing your account and reviewing sessions.
If the Requests Keep Coming
Check whether the service shows a device, browser, or location you recognize. Do not approve a request just to stop the notifications. If you think your password was exposed, change it through the genuine service and review the account’s security settings. For a work account, report the event through the authorized channel using the time and prompt wording. Keep the verification value out of the report.
If a provider shows unfamiliar activity after an unsolicited message, review connected devices and any recent changes to recovery information. Use its security controls to end sessions you do not recognize where appropriate. Avoid using any sign-in link supplied by the person who asked for the value. Open the provider from a saved address or its verified app.
Set Up a Reliable Way to Get Future Codes
If your service offers a standard app OTP, enroll it from the account’s security settings on a trusted device. Keep your old method available until you test the new one. Choose where you will keep an independent recovery option before you change the default factor.
Enroll and Confirm the Same Account
Begamob’s product page describes adding compatible accounts in through a QR code or a manual setup key and generating TOTP codes offline. This can help when several services use app codes and SMS delivery is unreliable. Scan only from the service’s verified enrollment page and label the entry with the right account identifier. Enter the first code back into the service to confirm enrollment.
Test Recovery Separately
Open a fresh sign-in in a trusted browser while keeping the original session. Check that the normal OTP works, then confirm which backup path the account offers. If backup information and the app are both stored on the same phone, its loss can affect both. Use a supported independent option where possible. NIST’s Digital Identity Guidelines explain that manually entered OTPs are not phishing-resistant. For accounts with a supported FIDO passkey or security key, consider that method too.
Before switching the default method on an important account, check what will happen to the previous one. Some providers allow it to remain enrolled, while others remove it during the change. Have a separately accessible recovery route so that a failed first test does not leave you with no way to sign in.
Keep the Code Flow Clear When You Change Devices
Before replacing a phone, list the important accounts that use an OTP. Record the service name and the method without recording secrets or current values. Check whether the app supports transferring entries and whether the provider permits enrollment of the new device while the old one still works. A successful phone migration does not establish that every service accepted the copied setup.
Move Before You Wipe
Keep the old device available for the first test on the new one. Sign into the most important account using the new entry. Then check the others individually. If an OTP only works on the old device, keep that method active while you use the provider’s official steps to register a replacement.
Recover at the Account Provider
If the old device is gone, start with an enrolled alternate method. A new app cannot calculate a valid OTP without the relevant enrollment data. Use the service’s recovery route or a work administrator if you are locked out. After you regain access, review the factors and remove any old device that should no longer be trusted.
When you rely on both app codes and delivered messages, test each type after a phone change. An app restore and a number transfer can finish at different times. Check the destination the service shows, then verify your everyday method from a fresh session. Keep an older enrolled factor until the new route works.
Common Questions About OTP
What Is an OTP Code?
It is a one-time password or verification value. The provider may deliver it by message or expect a value from an authenticator or token. Follow the active challenge and check the account and action before entering the code.
Is an OTP Always Six Digits?
No. Format and length depend on the service and method. The sign-in page may expect a particular number of digits or a recovery code in a different format. The label and destination tell you which value belongs there.
Can I Get an OTP Without My Phone?
Sometimes. A provider may offer a registered security key, a trusted device, or a backup code as an alternate method. If it requires a text sent to your old number and you no longer control it, use the service’s recovery path.
Can I Reuse an OTP?
Do not count on it. A provider may reject a value after it was accepted, after it expires, or after you start a fresh request. Get a current code for the active prompt and enter it only where the genuine service asks.
Does an OTP Make a Sign-In Phishing-Resistant?
No. A fake page can capture and relay a current code. NIST distinguishes manually entered codes from phishing-resistant methods. If the account supports a FIDO passkey or security key and you can recover it, consider using that option for sensitive accounts.
Final Thoughts
Get the OTP from the factor named on the account’s genuine sign-in page. Check which account, destination, and request are active before submitting a value. If a code expired, wait for a fresh app value or start a new provider challenge when necessary. Use an alternate method or official recovery when the registered factor is no longer available.
Keep the setup key private because it can generate more codes after the current one expires. Keep recovery information somewhere you can reach without your everyday phone. If someone asks you to send a verification value to them, go to the service directly to check the account. When you switch devices, test the new OTP and its fallback while the old route still works.
A short test during normal access can reveal an outdated phone number or an app entry registered to the wrong account. Check the alternate route at the same time. If it depends on a work administrator, save the help desk contact where you can reach it from outside the locked account.
Download Authenticator App
Secure your accounts with fast, reliable two-factor authentication. Download now and protect your login in seconds.
