
Google OTP App: Complete Guide to OTP, TOTP, and 2FA
Published August 8, 2026 · Updated October 8, 2026
What is the Google OTP app? Google Authenticator is a free mobile application that generates one-time verification codes for accounts supporting authenticator-based two-step verification (2FA). To use it, install Google Authenticator, enable an authenticator app in your account’s security settings, scan the provided QR code, and enter the six-digit code to complete setup.
Google Authenticator works on Android and iPhone. Once an account is enrolled, it can generate verification codes without an internet connection or mobile signal.
This guide covers downloading the app, adding accounts, transferring codes to a new phone, recovering access, and fixing invalid OTP errors.
How to Download the Google OTP App
The official Google OTP app is called Google Authenticator.
You can install it from:
Before installing, confirm that the developer is Google LLC.
Avoid downloading modified APK files or unofficial applications that imitate Google Authenticator.
Is the Google OTP App Free?
Yes. Google Authenticator is free to download and use.
You do not need a paid subscription to generate standard TOTP verification codes.
You can also use Google Authenticator without signing in to a Google Account, although account synchronization will not be available in that mode.
For a more detailed download walkthrough, see our Google Authenticator download guide.
Secure your accounts with fast, reliable two-factor authentication. Download now and protect your login in seconds.Download Authenticator App
📖 Read More Guides: Google Authenticator 2FA: Complete Guide to Two-Step Verification
How to Set Up Google OTP Verification Step by Step
Setting up a google otp app begins on the account you want to protect. The website or application must first support an authenticator application as a two-factor authentication method.
Step 1: Enable Two-Step Verification
Open the account’s security settings and look for Two-Factor Authentication, 2FA, 2-Step Verification, or Authenticator App.
For Google Accounts, Google places Google Authenticator within its 2-Step Verification options. Once configured, the application can generate a verification code when Google requests one during sign-in.
Step 2: Scan the QR Code or Enter the Setup Key
The service normally displays a QR code. Open your google otp app, choose the option to add an account, and scan it.
When QR scanning is unavailable, many services provide a text setup key that can be entered manually.
The QR code and setup key should be treated as sensitive credentials. Someone who gains access to the underlying secret may be able to reproduce future TOTP codes with another compatible authenticator.
Step 3: Confirm the First Code
The service will usually ask for the current number shown in the google otp app. Enter it before the current time window expires.
This confirmation proves that the authenticator and the verification server were provisioned with compatible information.
This process is commonly described as google otp verification. For a third-party service, it does not mean Google receives every code. The service that enrolled the TOTP credential normally performs its own verification.
Step 4: Save Recovery Options
After enrollment, save any recovery codes or alternative authentication methods provided by the service.
A google otp app improves security, but a recovery method remains important if your phone is lost, replaced, reset, or temporarily unavailable.
How to Set Up Google Authenticator for Your Google Account
You can also use Google Authenticator to protect a personal Google Account.
Enable Google Account 2-Step Verification
- Open Google Account Security.
- Sign in to your Google Account.
- Open 2-Step Verification.
- Complete any required identity verification.
- Find the Authenticator option.
- Follow Google’s setup instructions.
- Scan the displayed QR code using Google Authenticator.
- Enter the generated code to confirm enrollment.
The exact settings may vary depending on your Google Account configuration.
Google may also offer prompts, passkeys, security keys, and other verification methods.
Authenticator-generated codes are one available method, not the only way to protect your Google Account.
How a Google OTP App Generates Codes Without Internet
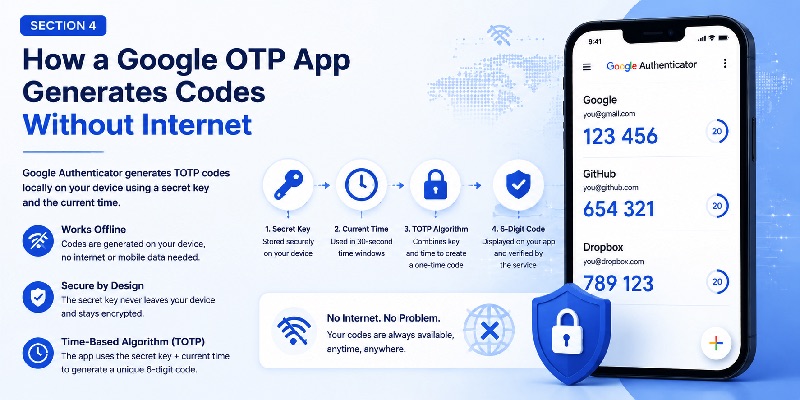
One of the most useful properties of a google otp app is offline code generation. Google confirms that Google Authenticator can generate verification codes without an internet connection or mobile service.
The App and Server Calculate Separately
During enrollment, the authenticator receives a secret. For TOTP, the google otp app combines that secret with a time-derived value to calculate a temporary numeric code.
The server performs a corresponding calculation. If the values match within the server’s permitted time window, authentication can continue.
This architecture explains why a code does not need to be downloaded from Google each time you sign in.
In a standard authenticator-based TOTP implementation, the phone does not query a remote google otp api simply to receive the next six-digit value. TOTP itself is calculated from the provisioned secret and time.
Why the Phone Clock Matters
Because TOTP uses time as a moving factor, your google otp app works best when the device’s date, time, and time zone are accurate.
Automatic date and time settings can help prevent significant clock differences between the device and verification system.
Sync Is Separate From Code Generation
Google Authenticator can currently synchronize verification codes across devices when users sign in to their Google Account. Google also states that synchronized Authenticator data is encrypted in transit and at rest.
Synchronization requires connectivity, but it is separate from the basic TOTP calculation. An enrolled google otp app can still calculate codes locally when the network is unavailable.
Google TOTP for Developers: Python, PyOTP, and API Use
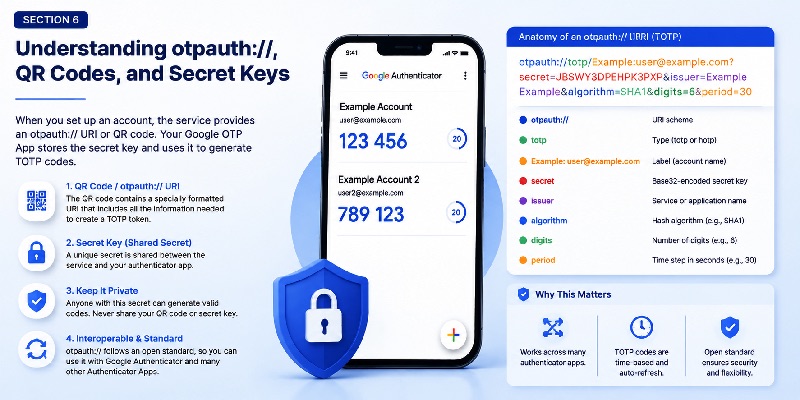
Authenticator applications are also relevant to developers who want to provide app-based 2FA inside their own services.
PyOTP and Google Authenticator Compatibility
PyOTP is a Python library supporting HOTP and TOTP. Its documentation specifically describes compatibility with Google Authenticator and includes methods for creating provisioning URIs suitable for authenticator enrollment.
That makes queries such as pyotp google authenticator and python otp google authenticator common when developers build TOTP authentication flows.
A typical architecture is:
- Generate a unique secret for the user.
- Create a compatible TOTP provisioning URI.
- Convert the URI into a QR code.
- Let the user enroll it in a google otp app.
- Request a current verification code.
- Verify the submitted code on the server.
- Protect the stored TOTP secret.
The google otp app acts as the code-generating side of this flow, while the application backend acts as the verifier.
Is There a Google OTP API?
The keyword google otp api can be confusing because “OTP” describes several different technologies.
Google provides Android APIs that help applications work with SMS verification codes. For example, its SMS Retriever-related APIs support SMS-based verification flows. Those APIs are different from Google Authenticator TOTP generation.
For authenticator-based TOTP, developers normally implement the standard on their own backend or use a trusted library.
They provision a secret compatible with the authenticator and validate the submitted code against the expected TOTP value.
The google otp app therefore does not need to expose every generated code through a remote Google endpoint.
Avoid Hard-Coding Secrets
Each user or authenticator enrollment should have its own appropriately generated credential. RFC 6238 specifies a unique secret for each prover and recommends protecting keys against unauthorized access.
Developers should also protect verification endpoints with controls such as rate limiting and secure transport rather than relying on the short lifetime of a TOTP alone.
📖 Read More Guides: How to Use Google Authenticator: Complete Setup and 2FA Guide
Google OTP App Compatibility With Bitwarden, KeePass, and LinOTP
A google otp app belongs to a much broader OTP ecosystem.
Because multiple applications implement compatible TOTP standards and provisioning formats, users are not necessarily restricted to a single authenticator product.
Compatibility does not mean every application provides identical storage, synchronization, migration, backup, or recovery behavior.
Bitwarden and TOTP
Bitwarden supports TOTP-based authenticator workflows. Its documentation also shows otpauth://totp/ provisioning data in authenticator import and export examples.
The phrase bitwarden totp google authenticator usually refers to compatible TOTP credentials being used or migrated between these ecosystems.
Authenticator exports should be handled carefully because they can contain information capable of generating future OTP values.
KeePass and OTP
KeePass documentation includes built-in functions for generating HMAC-based OTPs and time-based OTPs. It also supports configurable OTP parameters.
A query such as keepass otp google authenticator therefore usually relates to configuring KeePass with values compatible with an existing TOTP-enabled account.
A google otp app and KeePass can calculate matching TOTP values when they are configured with equivalent secret and algorithm parameters.
LinOTP and Google Authenticator
LinOTP supports HOTP and TOTP token enrollment. Its documentation provides a “Google Authenticator compliant” configuration that applies defaults designed for compatibility with Google Authenticator.
That is the connection behind searches for linotp google authenticator.
For organizations, these interoperable systems can be particularly useful because authentication can be managed server-side while users continue using familiar authenticator applications.
Invalid Google OTP Codes: Common Causes and Fixes
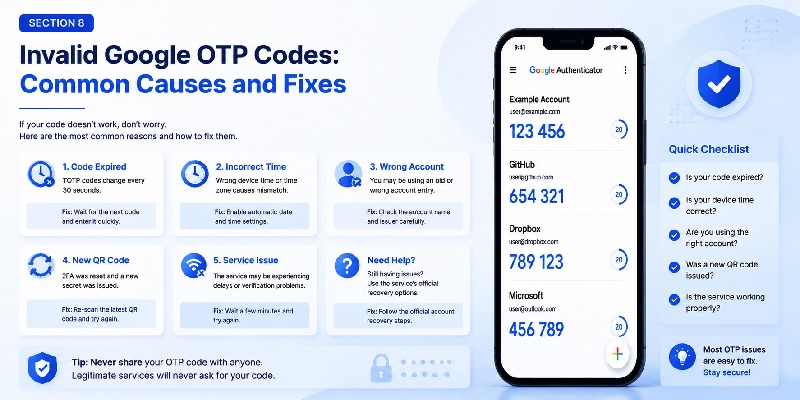
A google otp app may occasionally display a code that a website rejects.
This does not automatically mean the authenticator application has stopped working. The time window, enrolled secret, account selection, or server-side configuration may be responsible.
The Code Expired During Entry
TOTP values only remain current for a limited time window.
If only a few seconds remain, wait for the next number and enter it promptly. This is one common situation behind an invalid google code totp search.
The Phone Time Is Incorrect
Because TOTP derives its moving factor from time, significant clock differences can place the google otp app and verification server in different windows. RFC 6238 specifically discusses synchronization and allowable time-step windows.
Check the phone’s automatic date, time, and time-zone settings before assuming the token itself is corrupted.
The Wrong Account Entry Was Selected
Users with multiple authenticator entries for the same service can accidentally select an old token.
If the website’s 2FA configuration was reset, the older credential stored in the google otp app may no longer match the new server-side secret.
Check the account name and issuer before entering the code.
A Setup QR Code Was Replaced
Re-enabling authenticator-based 2FA may generate a new secret.
When a server expects the new credential but the authenticator still contains the previous secret, every displayed code can be rejected even though the numbers continue changing normally.
In that situation, enroll the current QR code or follow the service’s official account-recovery process.
The User Is Asking “What Is My OTP?”
A search such as google what is my otp does not have one permanent numeric answer.
Your OTP is the temporary value displayed for the relevant enrolled account at that moment.
Do not use random websites or ask another person to generate the code for you. Open your own authenticator or use the affected service’s official recovery method.
If the google otp app continues failing after the correct account and time settings have been verified, use the service’s supported recovery options rather than repeatedly guessing codes.
📖 Read More Guides: Google Password Verification: Passwords, 2FA, Passkeys and Authenticator
Security Best Practices for Google 2FA OTP and TOTP
A google otp app can strengthen account security, but the token itself and its recovery paths still require protection.
Protect the Enrollment Secret
Never publicly post a TOTP setup QR code, secret key, migration payload, or unprotected authenticator export.
If you believe a TOTP enrollment secret has been exposed, reset authenticator-based 2FA through the affected service and provision a new credential.
Use a Strong Device Lock
Protect the phone with an appropriate screen lock and keep the operating system updated.
If your google otp app uses account-based synchronization or backup, secure the account controlling that synchronization as well.
Keep Recovery Codes Separate
Recovery codes are useful when the authenticator device is unavailable.
Store them in a protected location that is not dependent on the same phone used to generate your normal OTP values. Google also provides alternative 2-Step Verification and recovery methods for situations where the primary verification option cannot be used.
Treat OTP as a Second Factor
A google otp app makes a stolen password less useful because an additional credential is required. Google describes 2-Step Verification as a way to help prevent unauthorized access even if a password is stolen.
However, users should still verify that they are signing in through the legitimate website or application.
Never Share a Current OTP on Request
Do not provide the current number from your google otp app to someone who contacts you unexpectedly and asks for a verification code.
Authenticator values should be entered only when you intentionally initiate a legitimate authentication flow.
📖 Explore Articles:
Google MFA App: Complete Guide to Secure Multi-Factor Authentication
How to Choose the Right Authenticator App
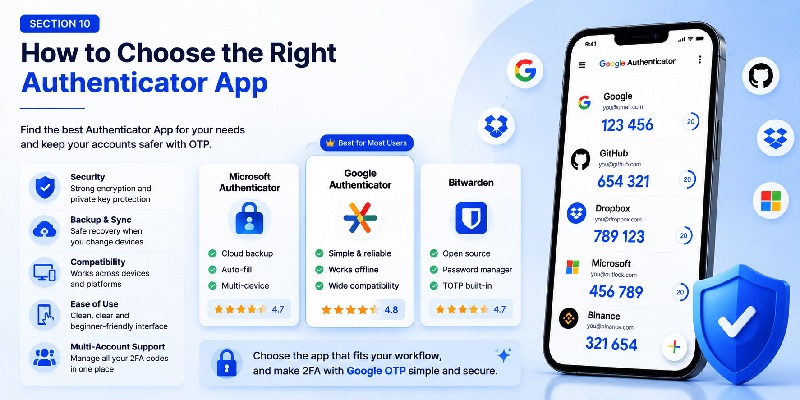
A google otp app such as Google Authenticator is a straightforward option for standard TOTP accounts.
Other products may combine authentication with password management, provide different synchronization approaches, or include administrative features designed for organizations.
When comparing an Authenticator App, consider five areas:
- Compatibility: Does it support the TOTP services you use?
- Migration: Can credentials be transferred safely when you replace your device?
- Backup or sync: Can authentication data be recovered, and how is access protected?
- Account labeling: Is it easy to distinguish several accounts for the same service?
- Recovery: What happens if the application or device becomes unavailable?
For most users, the core experience remains simple: enroll an account once, open the google otp app when the service asks for a verification code, and enter the current value.
The more important security considerations happen around that workflow: protecting the setup secret, maintaining secure recovery options, and selecting the correct account when several tokens are stored.
A properly configured google otp app provides a practical method for adding app-based two-factor authentication without depending on SMS delivery.
TOTP is designed for interoperability, allowing a verifier and authenticator to independently derive matching short-lived codes when both possess compatible secret and time information.
Whether you use Google Authenticator or another compatible tool, the core principles remain the same: protect the provisioning secret, maintain accurate device time, save appropriate recovery methods, and never expose active verification codes to untrusted parties.
For users evaluating otp google authenticator solutions, the safest starting point is to enable an authenticator through the official security settings of the account being protected.
For developers, google totp compatibility should be approached as a standards-based TOTP implementation rather than as a shortcut to a third-party code-generation service.
That distinction makes the entire authentication architecture clearer: the service owns its verification process, the authenticator protects the provisioned credential, and the temporary OTP provides an additional layer beyond the account password.
Download Authenticator App
Secure your accounts with fast, reliable two-factor authentication. Download now and protect your login in seconds.
