
Sage Authenticator App Setup and Recovery
Published November 17, 2026
By the Authenticator App Team
Last updated: November 2026
Set up a Sage authenticator app by signing in to your Sage product, opening the two-factor authentication prompt, and choosing the verification method shown for your account. If you prefer rotating codes, Sage’s guidance directs you to Authenticate a different way, then Authenticator app. Scan the QR code from the setup screen and enter the current six-digit value to finish. Sage Verify is another choice on supported flows and can send an approval notification when notifications are enabled.
If you have already enrolled and the Sage authenticator app is missing or inaccessible, start with the recovery options on the sign-in screen. Sage documents a 24-digit recovery value from initial enrollment and separately offers a recovery contact where supported. The fastest route depends on which method is registered and which fallback you can still reach.
Choose the Verification Method Sage Is Asking For
| What you see | Where the verification happens | What to do |
|---|---|---|
| An approval notification | Sage Verify on the registered device | Review the request and approve your own attempt |
| A six-digit app code prompt | The authenticator entry enrolled for your Sage account | Enter its current value |
| Text message or call listed as your method | The registered telephone number | Request delivery through Sage and follow the prompt |
| A recovery challenge | A saved recovery value or a verified recovery contact | Use the matching option shown on your account |
Start With the Login for Your Actual Product
Open Sage from the address you usually use for the product. Check the email and product before selecting a method, especially if you switch between clients, have separate work and personal addresses, or have been invited into a new organization. Sage’s documentation describes the Sage account sign-in, and a product may use its own access or organization controls after that sign-in.
If you are at a company identity provider instead, use the provider named on the screen and contact the administrator for that service when needed. A Sage authenticator app entry can verify the Sage account that enrolled it. A company sign-in may have a separate challenge, recovery route, and registered device even when you access Sage immediately afterward.
Compare Sage Verify With a Rotating-Code App
Sage’s guide to third-party apps recommends Sage Verify for its tap-to-approve notification experience. Pick that route if the sign-in offers it and your organization allows it. Check that notifications arrive before you depend on that device. When a request appears while you are doing something else, dismiss it and check your account from a trusted starting page.
Choose the Sage authenticator app code method when you want to read a current code and type it into the browser. Sage’s guidance names Google Authenticator and Microsoft Authenticator as examples. Use the exact method your Sage prompt expects. A phone that holds both apps, or multiple Sage entries in one app, can otherwise make a routine login look like a lockout.
Check the Method Before Changing Anything
A new device can still display an app icon after a restore even if the entry inside it did not transfer. Open the app and check whether the account is present. If you have two entries, compare their labels and open a clean Sage sign-in before removing either. One may be attached to a separate Sage login or to a replacement enrollment.
A phone that still receives a Sage Verify notification and a phone that has a working Sage authenticator app code provide different evidence. Test whichever prompt your account presents. If you manage several client organizations, test the intended Sage login first and verify the correct client context after the second factor succeeds.
Passwordless Multi Factor Authentication With Passkeys and Security Keys
Enroll a Third-Party App With the Sage QR Code
Keep the Setup Browser Open
Start a Sage sign-in on a trusted computer, enter your own login details, and select the setup option when Sage prompts you. Sage’s third-party app instructions list Set up authentication, Authenticate a different way, and Authenticator app. Wording can vary with the flow, so use the choices shown for your account and region.
On the phone, open the approved Sage authenticator app, add a new entry, and choose its QR scanner. Present the QR shown in the active Sage setup window. Keep the browser open until the first code has passed. If you lose the enrollment page, start the official flow again rather than scanning a saved image from a previous attempt.
Verify the First Code While the Entry Is New
Once the app creates the entry, compare its label with the Sage sign-in address. Enter the currently displayed value before its timer runs out. If the code is about to rotate, wait for the next one. A successful first Sage authenticator app code confirms that the app and Sage have registered corresponding values for that attempt.
Follow the remaining steps on the screen, including saving recovery material if it is displayed. Rename the entry in your app if that feature is available and would help you distinguish accounts. An internal label like Sage payroll or Sage client admin can be useful where it reveals no unnecessary information. The label does not change the enrollment.
Handle a One-Device Setup Carefully
If the QR appears on the same phone as the scanner, move the Sage setup to a trusted computer or second screen where possible. If the Sage page itself offers a supported manual setup value, follow its instructions and enter it directly in the approved app. Availability depends on the enrollment interface. Keep any setup value or QR away from messages, screenshots, and support tickets.
Before you call the Sage authenticator app setup complete, keep the original browser open and initiate a separate sign-in. Choose the account you just enrolled, enter the next live code, and verify that the expected product opens. The separate test is particularly valuable when an existing browser remembers you and normally skips a visible challenge.
Compare Apps for Sage’s Code-Based Enrollment
Use Your Organization’s Approved App First
Sage lists Google Authenticator and Microsoft Authenticator as examples of third-party apps for QR-based enrollment. Google Authenticator is a practical candidate when your organization already supports its backup and transfer model. Microsoft Authenticator can suit teams that already distribute it, provided you enroll Sage as a code entry and distinguish it from any Microsoft work approval prompt.
Where Sage offers a standard code-based enrollment and policy permits, is another option to evaluate for managing rotating codes. Compare whether the app scans the Sage QR successfully, whether its local unlock controls suit your device, and how you can regain access after loss. Review the actual recovery options before moving a working enrollment.
Match the Backup Model to the Account Owner
For a business login, verify who controls the account used to back up the app, if any. A personal app backup may be acceptable for an owner-managed device but may conflict with a company’s device policy. A Sage authenticator app on a managed device may also be wiped when an employee changes roles. Decide what the employee, owner, and help desk each need before changing phones.
A fallback must be available to the person authorized to sign in. A recovery mailbox behind the same missing phone may become unreachable during the same incident. Walk through who can access the fallback if the phone is broken, the SIM is replaced, or the device is removed from management. Use a separate, protected recovery method that fits the actual ownership of the Sage login.
Save a Recovery Route Before Moving Your Phone
Keep the 24-Digit Value Accessible
Sage’s sign-in help says that an enrolled user can use the 24-digit recovery key or code recorded when setting up two-factor authentication. Save the value as directed during enrollment in an approved place accessible without the registered phone. A business might use a restricted vault with an established emergency procedure. A sole proprietor can use a protected location they can reach independently.
The rotating Sage authenticator app code and the saved recovery value serve different purposes and go into different flows. When locked out, start with the official recovery choice and use the value only in the corresponding field. When Sage prompts you to update security settings after a recovery, record any replacement recovery material and remove obsolete copies.
Verify an Independent Recovery Contact
Sage’s U.S. account help describes adding a recovery phone number or recovery email through the Sage Account Login after authenticating. It specifies a different email address from the login email and recommends a separate phone number when text is already the primary method. Follow the settings shown for your region and verify the contact while the original method still works.
Test the practical side of that fallback as well. If both numbers live on the same handset, consider how you would regain access to the second number during a device outage. If your recovery email belongs to a business, check whether that mailbox remains available to the named user during travel or after a company phone is wiped.
Fix the Problem You Actually See
| Symptom | First check | Safe next step |
|---|---|---|
| The app has no Sage entry | Whether the entry moved or the current app is the enrolled one | Use a working original device or Sage recovery |
| The code is visible but rejected | Account label, device time, challenge type, and current code window | Try the next code once after correcting the mismatch |
| Sage Verify has no approval | Which registered device and which method Sage expects | Check notification permissions and follow the offered recovery route |
| A setup QR is missing | Whether you are at enrollment, regular sign-in, or a different provider | Return to the official setup or method-change flow |
| A colleague can sign in but you cannot | Whether each person has separate credentials and organization access | Have the owner verify your individual access separately |
Correct the Clock and the Account Label
A valid-looking code can belong to a different Sage sign-in or have expired while you were entering it. Select the entry for the correct address, enable automatic device date and time where permitted, and wait for a fresh value. Keep the current Sage challenge open as you enter it. If it is still rejected, check whether Sage asked for a delivered code or an approval instead.
If the Sage authenticator app worked before a device transfer and an original phone still has the entry, test that original entry from the official browser flow. This identifies whether the new app is missing the current enrollment. If both fail and the login details are correct, use the registered fallback or follow Sage’s official assistance process for your product.
Preserve Access During a Payroll Deadline
If you still have a working Sage session, avoid closing it before verifying an alternate route. Check the account address and identify another authorized person who can cover the business process if access changes. In an organization where only one person can sign off payroll, give the account owner time to verify a replacement before the next deadline.
If you need support, state the product, account region, sign-in method shown, whether the old phone is available, and whether you can reach the verified recovery contact. Include the exact wording of the error if it reveals no secrets. A screenshot of the enrollment QR or current Sage authenticator app code would expose material you need to keep private.
Treat Unexpected Requests as a Separate Issue
If Sage Verify displays an approval you did not initiate, let it expire or reject it when that option is available. Open Sage through your usual login address to review the account and check with your security team when applicable. A recovery attempt initiated by a stranger or a suspicious message asking you for the 24-digit value requires a different response from a mistyped code.
If you believe the Sage authenticator app QR or recovery material was shared, use the account’s official process to replace the exposed method or ask Sage how to proceed. Review the registered contacts and follow your organization’s incident procedure. When an employee’s device is missing, coordinate the account action and device handling rather than postponing both until the phone turns up.
Test the Sage Authenticator App on the Replacement Phone
Replace a Working Method in a Quiet Window
With the old phone still usable, open the relevant Sage account security options and look for the official flow for changing the registered factor. Sage’s change-method guidance says the account uses one primary method at a time, so prepare the replacement before committing to the change. Complete the new enrollment while you can still access any prompt that requires the previous factor.
If you switch from Sage Verify to a Sage authenticator app entry, test the new sign-in using the code challenge. If you switch to Sage Verify, check that an approval request arrives and that you recognize its source. The replacement test should be a separate sign-in with the account you actually use, subject to your organization’s normal session rules.
Verify Access to the Intended Business Record
After the replacement passes, open the expected Sage product and check the organization and task you need. A successful login proves the account passed its challenge. It does not tell you whether the product invited the right person, whether the employee has the required role, or whether the browser opened the right client file.
Before handing in the old phone, verify the current recovery option, remove obsolete copies when the account change is complete, and follow your employer’s device-return procedure. If the team records the handover, record the factor type and test outcome only. Keep live values, the QR, and the saved recovery code out of operational notes.
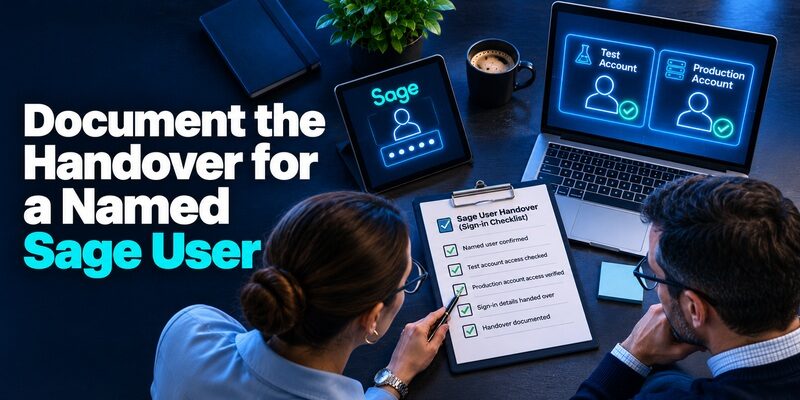
Document the Handover for a Named Sage User
Keep a Test Account Separate From the Live Record
If your team rehearses a phone change, choose an account it is authorized to use for the exercise. A successful test with a demonstration user helps verify that the new Sage authenticator app can scan and produce a code. Repeat the sign-in for the actual user before removing that person’s old method. The production user may have different recovery contacts or a product entitlement absent from the test account.
When administrators coordinate the switch, agree beforehand who will handle recovery if the replacement fails. An owner can confirm identity and access, while a device administrator can check installation and time settings. The person who owns the account should enter their own Sage authenticator app value privately.
Check the Contact After an Organization Change
When a person leaves a company or changes email domains, review which Sage login the product uses and where notices or recovery messages go. An account may still appear in a saved browser even after its old email route no longer works. Review the registered contact with the account owner before the old mailbox is closed.
Leave the owner a record of the approved sign-in page, the chosen method, and the route for help. Record the last successful test of the Sage authenticator app if your organization tracks such changes. That gives the next support person a baseline without sharing a code.
Final Thoughts
Choose the Sage authenticator app method shown for the correct account, finish enrollment by confirming the first code, and test a separate sign-in while you still have a working fallback. Sage Verify is appropriate if you want supported approval notifications. Third-party rotating codes make sense when that is the method you want and your organization permits it.
If access fails, use Sage’s official recovery prompt with the saved recovery value or the verified recovery contact. Check that the expected Sage product and organization open afterward. The best time to confirm those recovery details is while your original method still works.
Download Authenticator App
Secure your accounts with fast, reliable two-factor authentication. Download now and protect your login in seconds.
