GitHub 2FA Authenticator: How to Set Up and Protect Your Account
Published August 23, 2026 · Updated October 1, 2026
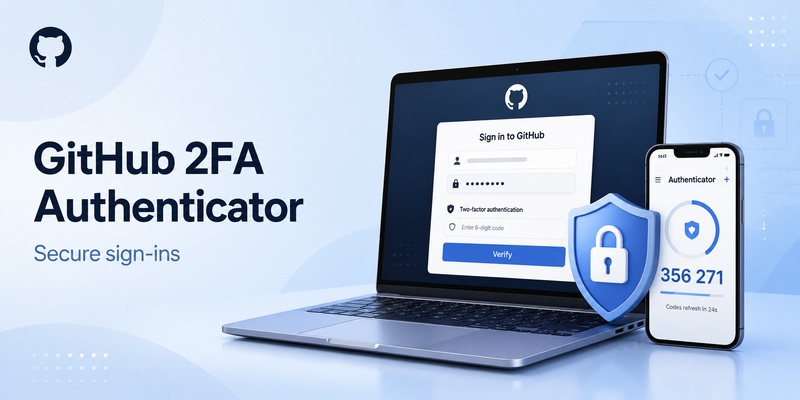
A github 2fa authenticator is a time-based authentication method that adds another verification step to your GitHub login. Instead of protecting an account with only a username and password, two-factor authentication requires a second credential before access is granted.
For many GitHub users, that second credential is a temporary six-digit code generated by an authenticator application.
GitHub supports time-based one-time password, or TOTP, applications on mobile devices and computers. GitHub specifically recommends using a TOTP app for 2FA rather than SMS because TOTP applications are generally more reliable and avoid several weaknesses associated with text-message authentication.
A github 2fa authenticator can therefore be Google Authenticator, Microsoft Authenticator, a password manager with TOTP support, or another compatible application.
GitHub is largely app-agnostic for TOTP authentication. Its documentation states that users can choose their preferred TOTP application rather than being required to install a GitHub-branded authenticator.
That makes setting up a 2fa authenticator github workflow relatively flexible.
For developers, this additional protection is particularly valuable because a GitHub account may provide access to source code, private repositories, organizations, packages, automation workflows, and other development resources.
GitHub began requiring many users who contribute code on GitHub.com to enable 2FA as part of its account-security initiative beginning in March 2023.
Whether 2FA is mandatory for your account or simply enabled voluntarily, understanding your github 2fa authenticator configuration helps prevent both unauthorized access and accidental account lockouts.
1. Quick Answer: How to Set Up GitHub 2FA With an Authenticator App
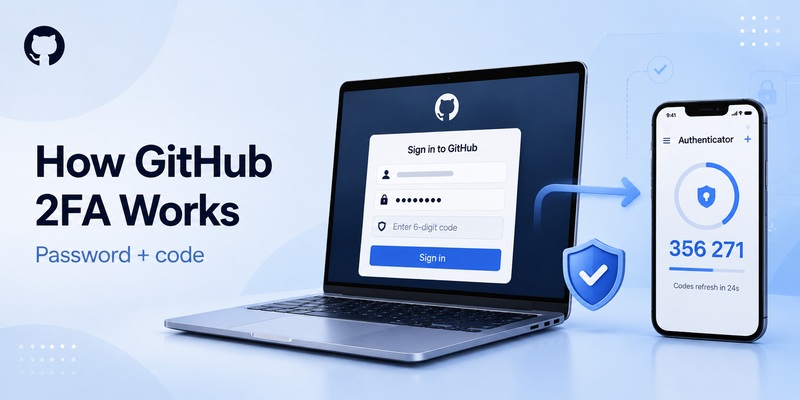
To set up GitHub 2FA authenticator, sign in to GitHub and open Settings → Password and authentication → Two-factor authentication. Choose the authenticator app option, scan the QR code with a TOTP-compatible app, then enter the six-digit code generated by the app.
After GitHub verifies the code, save the recovery codes before finishing setup. It is also worth adding a passkey or security key as an additional recovery or authentication method.
GitHub currently recommends TOTP apps as a primary two-factor authentication method and encourages users to configure additional authentication and recovery methods to reduce the risk of account lockout.
Download Authenticator App
Secure your accounts with fast, reliable two-factor authentication. Download now and protect your login in seconds.
2. How to Set Up GitHub 2FA With an Authenticator App
Step 1: Open GitHub Settings
Sign in to GitHub, click your profile picture, and select Settings.
Step 2: Open Password and Authentication
Under Access, choose Password and authentication.
This area contains GitHub’s password, two-factor authentication, passkey, security key, and recovery settings.
Step 3: Enable Two-Factor Authentication
Find the Two-factor authentication section and select Enable two-factor authentication.
GitHub may ask you to verify your identity before continuing.
Step 4: Choose an Authenticator App
Choose the TOTP authenticator option.
GitHub will display a QR code that contains the information needed to configure the authenticator.
Step 5: Scan the QR Code
Open your authenticator app and add a new account.
Choose the QR scanning option and scan the code displayed by GitHub. If scanning is not possible, GitHub also provides a setup key that can be entered manually.
Once added, the authenticator will begin generating a six-digit GitHub code.
Step 6: Verify the Code
Return to GitHub and enter the current six-digit code from the authenticator app.
This confirms that GitHub and your authenticator are correctly paired.
Step 7: Save Your Recovery Codes
After the authenticator is verified, GitHub provides recovery codes.
Save them somewhere secure before completing setup. Do not store your only copy on the same phone that runs the authenticator app.
A password manager, encrypted file, or secure printed copy is more useful because it remains available if the phone is lost.
Step 8: Complete Setup
Confirm that you saved the recovery codes and finish enabling 2FA.
At this point, your authenticator app becomes part of the normal GitHub sign-in process.
3. How GitHub TOTP Codes Work
A GitHub TOTP code is a short-lived verification code generated from two things: a secret stored by the authenticator and the current time.
The code changes automatically, usually every 30 seconds.
When GitHub asks for 2FA, open your authenticator app, find the GitHub entry, and enter the current code before it expires.
Because the code is generated locally, you generally do not need an active internet connection on the phone just to view it.
 Discover Helpful Guides: 2FA Authenticator App: Complete Guide to Setup, Use, Download, and Secure Your Accounts
4. Using Google Authenticator with GitHub 2FA
Yes, you can use Google Authenticator as your github 2fa authenticator.
GitHub allows compatible TOTP apps, so Google Authenticator can generate the six-digit codes required for GitHub login.
The github 2fa google authenticator setup follows the normal GitHub TOTP process.
Open GitHub’s Password and authentication settings, choose authenticator-based 2FA, and display the QR code.
In Google Authenticator, choose the option to add an account and scan the QR code.
If you are researching adding accounts to google authenticator, GitHub is simply another standard TOTP account. After scanning the setup QR code, the GitHub entry appears alongside your other authentication accounts.
The resulting 2fa code google authenticator displays for a limited period before being replaced with another six-digit code.
For users asking how to use google authenticator 2fa with GitHub, the login process is simple: enter your GitHub password, open Google Authenticator, find the correct GitHub account, and enter the current code.
A common mistake occurs when people have multiple GitHub profiles inside Google Authenticator.
Your github 2fa authenticator code is account-specific. A code generated for one GitHub account cannot authenticate another.
GitHub’s troubleshooting guidance specifically recommends checking that you are using the correct account entry when a TOTP code repeatedly fails.
5. Test GitHub 2FA After Setup
Do not wait until you actually need GitHub urgently to discover that the authenticator was configured incorrectly.
After setup, open a private or incognito browser window and sign in again. Enter your GitHub password, then use the current code from your authenticator.
If the login succeeds, you have confirmed that the basic TOTP flow works.
GitHub also uses a post-setup checkup period for newly configured 2FA accounts, so testing early is useful.
6. GitHub Recovery Codes: Why They Matter
Recovery codes are emergency credentials for situations where your normal 2FA method is unavailable.
For example, they can help if your phone is lost, the authenticator app is deleted, or a device migration fails.
Each recovery code is intended for one-time use.
GitHub currently provides a set of recovery codes that you should store separately from your authenticator device.
If the codes are exposed or mostly used, generate a new set. When a new set is created, the previous recovery codes become invalid.
Discover Helpful Guides: 2FA Authenticator Chrome: How to Set Up Secure Two-Factor Authentication in Your Browser
7. Where to Find GitHub Recovery Codes
If 2FA is already enabled, open:
Settings → Password and authentication → Recovery codes
From there, GitHub lets you view and store the current recovery codes.
Keep them in a location you can access without the phone running your authenticator app.
The point of a recovery code is to survive the loss of your main authentication device.
 Explore More Useful Guides: 2FA Authenticator Free: How to Choose and Use a Free Authenticator App Safely
8. TOTP vs Passkey vs Security Key
| Method | Main role | Typical use |
|---|---|---|
| TOTP authenticator | Primary 2FA | Password + six-digit code |
| Passkey | Passwordless authentication | Sign in with device/passkey |
| Security key | Additional second factor | Password + physical key |
| Recovery code | Emergency access | Recover access when 2FA is unavailable |
These methods are complementary rather than mutually exclusive.
For most users, a practical setup is:
TOTP authenticator + saved recovery codes + one additional method such as a passkey or security key.
Explore More Useful Guides: How to Use 2FA Authenticator: A Complete Step-by-Step Guide for Better Account Security
9. GitHub Authenticator Code Not Working
If GitHub rejects the code, first confirm that you are viewing the correct GitHub entry in your authenticator app.
If the current code is about to expire, wait for the next one and try again.
Another common cause is incorrect device time. TOTP depends on time synchronization, so the phone’s date, time, and time zone should be set automatically.
Also remember that GitHub does not send a TOTP code to your phone. The authenticator app generates it locally.
If you are waiting for an SMS while using the authenticator method, you may be looking for the wrong type of code.
Explore More Useful Guides: 2FA Authenticator APK: Safe Download, Installation, and Setup Guide for Android
10. GitHub 2FA Security Best Practices
A github 2fa authenticator significantly improves account security, but the way you configure it matters.
First, securely store your recovery codes immediately after enabling 2FA.
Second, consider adding more than one authentication method.
GitHub recommends multiple 2FA and recovery methods to reduce lockout risk.
Third, protect the device that contains your authenticator with a secure PIN, password, or biometric lock.
Fourth, never share your TOTP setup secret or QR code.
Fifth, confirm that your authenticator’s time settings remain synchronized automatically.
For even stronger account protection, GitHub supports security keys and passkeys. GitHub notes that passkeys can satisfy both password and 2FA requirements, while security keys can be configured as an additional method after 2FA is enabled.
A practical security setup might therefore combine github 2fa authenticator with secure recovery codes and a hardware security key or passkey.
This creates multiple ways to authenticate without depending entirely on one phone.
11. Frequently Asked Questions
What authenticator app works with GitHub?
GitHub supports standard TOTP-compatible authenticator applications.
How do I enable GitHub 2FA with an authenticator app?
Go to Settings → Password and authentication → Enable two-factor authentication, scan GitHub’s QR code with a TOTP app, enter the generated six-digit code, and save your recovery codes.
Where are GitHub recovery codes?
Open Settings → Password and authentication → Recovery codes.
Can I use a passkey instead of an authenticator code?
After 2FA is configured, GitHub supports passkeys as an additional sign-in method. In supported flows, a passkey can satisfy both password and 2FA requirements.
Can I use a hardware security key with GitHub?
Yes. GitHub supports compatible WebAuthn security keys as an additional authentication method.
What if I lose my phone?
Use a previously configured recovery code, passkey, security key, or another available recovery method.
Can GitHub Support simply remove 2FA if I lose everything?
You should not rely on that. If all valid 2FA credentials and recovery methods are lost, recovery may not be possible.
Final Thoughts
A github 2fa authenticator is one of the most practical ways to strengthen a GitHub account beyond password-only security.
GitHub supports standard TOTP authentication, which means developers can choose from Google Authenticator, Microsoft Authenticator, and many other compatible tools rather than being locked into one application.
Setting up github 2fa authenticator requires only a few steps: open GitHub’s password and authentication settings, enable 2FA, scan the QR code, enter the generated six-digit code, and securely store the recovery codes.
The recovery step should never be skipped.
A lost phone is inconvenient, but a lost phone combined with missing recovery methods can become a serious account-access problem. GitHub explicitly warns that Support cannot simply restore accounts when users lose both their 2FA credentials and recovery options.
If a github 2fa authenticator code fails, first confirm the correct account, synchronize the device clock, wait for a fresh 30-second code, and enter it promptly.
For users who want stronger protection, GitHub also supports additional authentication methods including security keys, GitHub Mobile, and passkeys.
The strongest setup is not simply turning on github 2fa authenticator once and forgetting about it. It is combining a reliable authenticator with secure recovery codes, additional authentication options, and careful protection of the device that holds your TOTP credentials.
Download Authenticator App
Secure your accounts with fast, reliable two-factor authentication. Download now and protect your login in seconds.